Microsoft exposes how USDT-funded phishing network targeted 75,000 organizations
Domain seizures and account shutdowns hit YAM Store and phishing-kit services, while reported asset freezes remain unquantified. Read the full story on CryptoSlate Understand the crypto stories that matter and what to watch next. Get The Catalyst in your inbox
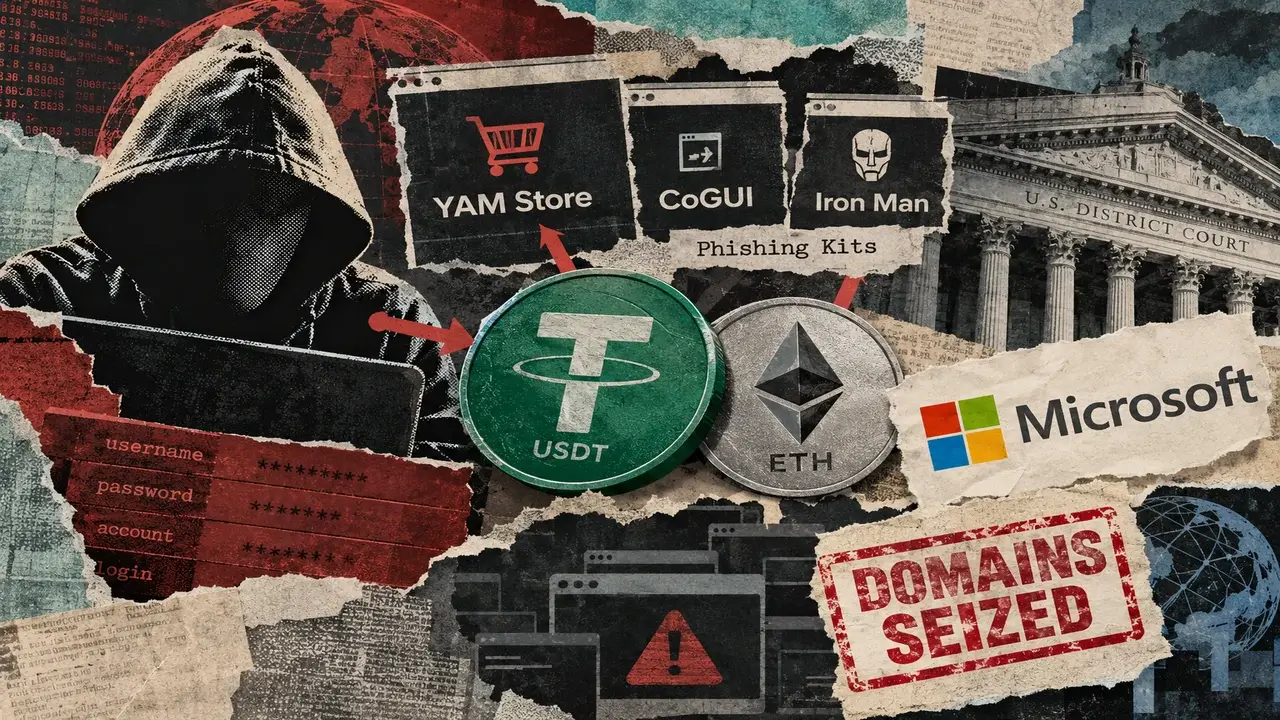
Microsoft disclosed a phishing network funded by USDT that targeted roughly 75,000 organizations, leading to domain seizures and shutdowns of services including YAM Store and phishing-kit providers. Reported asset freezes tied to the operation have not been quantified. The story highlights illicit use of stablecoins, a recurring regulatory talking point that could weigh modestly on sentiment around USDT and stablecoin oversight, though no direct market mechanism or price impact is identified.