Eclair patches a browser attack that could send commands to your Lightning node
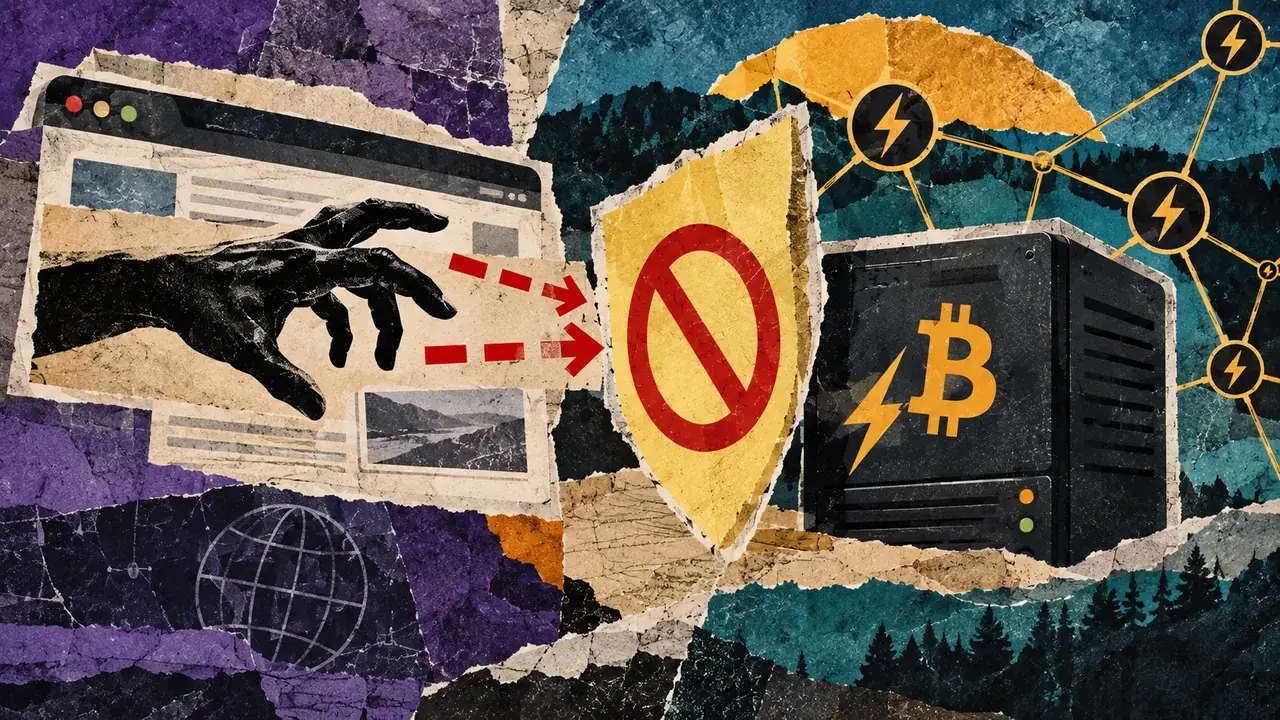
The Oct. 15 release blocks a cached-authentication route to Eclair's API and requires direct browser interfaces to add a backend. Read the full story on CryptoSlate Understand the crypto stories that matter and what to watch next. Get The Catalyst in your inbox
AI summary
Eclair released an Oct. 15 update patching a browser-based attack vector that could have allowed commands to be sent to a user's Lightning node via a cached-authentication route to its API. The fix blocks that path and now requires direct browser interfaces to add a backend. The issue is a security hardening update for node operators rather than a market-moving event, though it highlights ongoing operational risks in Lightning infrastructure.